AI agent governance: A practical guide to risk, trust, and compliance
Summary
AI agent governance is the set of policies, runtime guardrails, monitoring, and human oversight that keeps autonomous AI agents inside defined boundaries. It lets enterprises block unsafe actions before they run, reconstruct any agent decision later, and show regulators evidence of control. Effective governance is built into the agent platform, so it scales with every new agent.
What’s on this page
On November 16, 2026, Gartner published a survey of 298 infrastructure and operations leaders in the US and UK. 95% said their organization had faced at least one AI agent-related incident in the past 12 months. Yet 70% believed their AI agents operate within safe boundaries, and 57% called their own governance weak. (Gartner, November 2026)
Deloitte found the same gap from the business side. Nearly three-quarters of companies plan to deploy agentic AI within two years, but only 21% have a mature model for agent governance. Most lack clear boundaries for which decisions an agent can make alone and which need human approval. (Deloitte, State of AI in the Enterprise, January 2026)
Here is what one of those incidents can look like. A bank's operations team builds a dispute agent on a no-code tool. It reads each claim, applies the refund policy, and credits the account. On a Friday, someone edits the refund policy in the agent's knowledge base, and the agent reads the new wording differently than the policy team intended. By Monday, it has approved more than 3,000 refunds, against a normal weekend of a few hundred. Compliance cannot see which policy version the agent applied. Risk finds that the refund limit lived only in a prompt. The CIO learns the only way to pause the agent is to switch off the whole dispute channel. (This example is illustrative. Each gap in it is common.)
Gartner expects the cost of these gaps to grow. Without strong governance, it predicts 40% of infrastructure and operations organizations scaling AI will suffer a business-critical service disruption by 2028.
AI agent governance closes that gap. It turns instructions into controls the runtime enforces, records every agent decision in a form people can trust, and keeps a human able to step in at machine speed.
Key takeaways
- In a Gartner survey, 95% of organizations had an AI agent incident in the past year (November 2026). Deloitte finds only 21% have mature agent governance (January 2026).
- AI agent governance prevents violations at runtime. Courts hold companies liable for what their AI says and does.
- Three pillars hold it up: risk management, trust and responsible AI, and regulatory compliance.
- The EU AI Act is in force. Fines reach €35 million or 7% of global turnover for prohibited practices, and €15 million or 3% for most other breaches, including high-risk duties (EU AI Act, Article 99).
- Buyers should assess eleven capabilities, from guardrails and decision provenance to drift detection and automatic audit evidence.
This guide is for enterprise leaders who deploy, or plan to deploy, AI agents in production. It explains what AI agent governance requires, why traditional AI governance falls short, and how to evaluate a platform's governance capabilities.
What is AI agent governance?
AI agent governance is the combination of organizational structures and technical controls that keeps autonomous AI agents safe, accountable, and aligned with business intent, legal duties, and public expectations over time. It covers policies, guardrails, monitoring, and oversight. Put simply, AI agent governance is how an enterprise keeps control of systems that reason, decide, and act without asking permission first.
An AI agent is software that perceives its environment, reasons through options, and takes actions on its own, often across several systems. Because agents act, AI agent governance must work at the moment of action. A policy document cannot stop an agent mid-transaction. A runtime guardrail can.
How do you know AI agent governance works in practice?
Effective AI agent governance is measured by agent behavior under real operating pressure. Three tests show whether it works:
- Prevention. The platform blocks a prohibited action before it runs, rather than detecting it afterward.
- Reconstruction. A team can explain why an agent made a decision six months later.
- Intervention. A human can pause, override, or shut down an agent that operates at machine speed.
The bank in the opening scenario failed all three. A prompt held the refund limit, so nothing blocked the spike. The logs recorded actions but not reasons. And the only way to stop the agent was to stop the whole channel. A governance program that fails these tests looks complete on paper and offers little protection in production.
Why governance is measured by behavior, not documentation
In practice, effective AI agent governance is measured by three questions:
- Can you prevent violations before they happen, not just detect them after?
- Can you reconstruct why an agent made a decision six months later?
- Can you intervene meaningfully when agents operate at machine speed?
The difference between governance that works and governance that looks good on paper comes down to these operational realities.
Why do traditional AI governance frameworks fail for AI agents?
Traditional AI governance assumes a human makes the final decision. That assumption breaks when AI agents act on their own. The classic cycle runs in five steps: train a model, validate performance, assess bias, deploy, and monitor for drift. It works for predictive AI because the model only recommends and a person decides. Accountability stays clear, and review can be periodic.
AI agents take the action themselves. They often coordinate with other agents, run outside business hours, and decide in milliseconds. Human review still exists, but it cannot keep pace. When something goes wrong, the decision trail is harder to follow and accountability is harder to assign.
No-code agent builders add a second pressure. Business users can now build agents with access to live systems and sensitive data. Many of these citizen developers have never designed guardrails, data boundaries, or audit trails.
The table shows what changes and what governance must do in response.
What are the three pillars of AI agent governance?
AI agent governance rests on three pillars: risk management, trust and responsible AI, and regulatory compliance. The pillars depend on each other. Trust requires managed risk, and compliance evidence requires both. Teams that run the three as separate programs find gaps when auditors ask for evidence that spans all of them.
- AI risk management prevents material harm. It detects when agent behavior drifts into unsafe territory and manages cascading failures, goal misalignment, and emergent behavior that no one programmed.
- Trust and responsible AI cover the human side. Customers, employees, partners, and regulators need to know when an agent decides, why it decided, and when a human can step in. Without trust, agents stay confined to low-stakes work.
- Regulatory compliance covers the legal duties. The EU AI Act and state and industry rules require documentation, auditability, and demonstrable control.
These three pillars shape every later choice: which AI agent platform to buy, which governance infrastructure to fund, and which observability to require.
Why is AI agent governance now a legal and business requirement?
AI agent governance is now required for three reasons: regulation, legal liability, and the probabilistic nature of AI agents. Governance also speeds deployment once it is in place, because approvals move faster when controls are proven.
Which regulations apply to AI agents?
The EU AI Act is the most comprehensive AI law in force. The EU AI Act sets mandatory duties for high-risk AI systems, including risk management, data governance, transparency, and human oversight. High-risk uses include credit decisions, hiring, and access to essential services.
Fines under EU AI Act Article 99 have three tiers:
- Up to €35 million or 7% of worldwide annual turnover, whichever is higher, for prohibited AI practices.
- Up to €15 million or 3% for breaches of most other duties, including high-risk system obligations.
- Up to €7.5 million or 1% for supplying incorrect information to authorities.
As of November 2026, the EU's Digital Omnibus agreement moves the main high-risk obligations for stand-alone (Annex III) systems from August 2, 2026, to December 2, 2027.
Whether an agent counts as high-risk depends on its use. An HR agent that screens resumes and influences hiring decisions falls into the high-risk employment category. A customer service agent that processes refunds may raise similar questions if its decisions limit a customer's access to essential services.
In the United States, AI rules are emerging state by state and city by city:
- Colorado's AI Act targets algorithmic discrimination in consequential decisions.
- New York City's Local Law 144 requires bias audits for automated employment decision tools.
- California rules on algorithmic discrimination.
Each jurisdiction sets different duties and timelines. An enterprise that deploys AI agents across markets must meet several frameworks that do not align.
What legal liability do AI agents create?
Courts are now deciding who is responsible when AI systems cause harm. In Moffatt v. Air Canada (2024 BCCRT 149), Air Canada's website chatbot told a customer he could claim a bereavement fare after travel, which contradicted the airline's own policy. Air Canada argued it could not be held liable for its chatbot's answer. British Columbia's Civil Resolution Tribunal rejected that argument, found the airline liable for negligent misrepresentation, and ordered it to pay damages. (American Bar Association, Business Law Today, February 2024) The principle is clear: an enterprise owns what its AI says and does. Organizations also face lawsuits over algorithmic bias in lending and hiring.
Without documented decision rights, complete audit trails, and oversight mechanisms, an enterprise cannot defend an agent's decision when something goes wrong. The practical choice is between building governance before an incident or after one.
Why do AI agents need continuous governance?
AI agents are probabilistic systems. The same input can produce different outputs, and behavior shifts as environments, data, and interactions change. Behavior that passes testing at deployment can degrade later or combine with other agents in unexpected ways.
Traditional software testing assumes deterministic behavior, so it cannot certify an AI agent once and for all. Continuous monitoring, behavioral analysis, and fast intervention are the default operating condition for agentic AI.
How does AI agent governance speed up deployment?
Mature AI agent governance shortens approvals. When policies are clear, controls are proven, and risks are managed, legal, security, and compliance teams sign off faster. The first agent requires building the governance foundation. Later agents inherit those patterns and move through review in weeks instead of months.
Most organizations that struggle to scale agentic AI are held back by uncertainty: what is safe, what is allowed, and what could fail in ways they cannot explain.
What governance questions do enterprise buyers ask about AI agents?
Enterprise buyers ask six recurring questions about AI agent governance. Each question below has the short answer a credible platform should give.
1. How do AI guardrails prevent violations instead of only detecting them?
AI guardrails prevent violations when the platform enforces them at runtime. A runtime guardrail blocks a prohibited action before it executes. Strong guardrails combine fixed constraints with adaptive controls that adjust an agent's authority based on context and risk.
2. How do you stop AI agents from hallucinating or acting on wrong information?
Ground AI agents in approved knowledge sources. Require validation or source attribution for factual claims. Add confidence checks or verification steps before an agent acts on an output in a high-impact scenario.
3. How is AI agent bias monitored over time?
Monitor AI agent fairness continuously in production. Track outcomes across relevant groups, and define a remediation path before disparities appear, so the team knows what to do when they do.
4. How are multi-agent workflows governed?
Govern multi-agent workflows at the system level. That means visibility into how agents interact, controls on coordination patterns, and the ability to stop a workflow when collective behavior becomes unsafe.
5. How do you protect sensitive data that AI agents can access?
Treat each AI agent as a privileged insider. Enforce strict identity, access control, data minimization, and output filtering to prevent unauthorized exposure.
6. What happens when AI agents behave unexpectedly together?
Expect emergent behavior in multi-agent systems. AI agent governance should detect, bound, and isolate problem patterns instead of assuming agents will always behave predictably.
How should buyers evaluate an AI agent platform's governance?
Buyers should weigh an AI agent platform's governance capabilities as heavily as its core features. A capable platform that cannot be governed creates risk and liability. The eleven areas below form an evaluation framework for whether a platform can run autonomous agents safely at scale.
Guardrails: are controls enforced by the platform?
AI guardrails should be enforced by the platform's architecture and should stop prohibited actions before execution. Strong platforms apply guardrails in four places:
- Input controls limit what data agents can access and process. They reduce exposure to adversarial attacks and prompt manipulation.
- Process controls shape how agents decide. They enforce confidence thresholds, reasoning steps, or multi-factor validation.
- Output controls prevent sensitive data leakage, inappropriate responses, and regulatory violations.
- Action controls limit what agents can execute, through transaction limits, scope boundaries, and escalation triggers.
Observability: can you see what agents do and why?
Agent observability tracks behavior, beyond system health. Effective platforms give continuous visibility into:
- agent actions, decisions, and data access
- behavioral anomalies and policy violations
- performance, cost, and security signals
Decision provenance is the record of what an agent considered when it decided. Buyers should be able to reconstruct the information an agent used, the alternatives it weighed, the policies that applied, and its confidence level. The platform should also let teams intervene quickly through rollbacks, enforcement, or shutdowns.
Evaluation and testing: how do you test a probabilistic agent?
AI agent evaluation measures statistical consistency over time, because the same input can produce different outputs. Pass or fail tests alone do not fit. Buyers should look for:
- accuracy and reliability thresholds tied to decision risk
- continuous evaluation across the agent lifecycle
- separate testing of single agents and multi-agent interactions, where many failures appear
Data security: are agents governed like privileged users?
AI agents with system access should be governed like high-privilege users. Effective AI agent security includes:
- a unique identity and a named owner for each agent
- strict access control and data minimization
- output protections that stop sensitive information disclosure
- defenses against AI-specific threats such as prompt injection and data poisoning
The goal is least privilege by design.
Supply chain: what happens when a model or tool changes?
AI agent behavior depends on components that change outside your control:
- foundation models, which providers update often
- third-party APIs and tools that agents call
- open-source libraries and dependencies
The key buyer question is: what happens when a model provider updates its model and my agent starts behaving differently? Required capabilities:
- Version pinning locks an agent to a specific model version.
- Pre-production testing checks model updates before release.
- Rollback restores the previous version when an update causes problems.
- Approval workflows control which new tools an agent can use.
Drift management: how do you catch agents that degrade over time?
Drift is a change in agent performance or behavior after deployment. AI agent governance should detect four types of drift:
- Data drift. Input distributions change, for example when customer demographics shift.
- Concept drift. The relationships the agent relies on change, for example when fraud patterns evolve.
- Performance drift. Accuracy degrades over time.
- Behavioral drift. Agent strategies change in unintended ways.
Platforms should also manage nondeterministic behavior through confidence thresholds and acceptable variance ranges, and govern models through versioning, monitoring, and controlled updates.
Bias and fairness: what happens after bias is detected?
Bias can emerge after deployment through feedback loops, even when initial testing found none. Effective governance defines fairness metrics, monitors outcomes across relevant groups, and sets a remediation workflow in advance:
- Contain. Reduce agent autonomy at once and force human review.
- Assess. Measure the scope, such as how many customers are affected.
- Find the root cause. Identify whether a feedback loop, data drift, or model issue caused it.
- Correct. Retrain, adjust policy, or update data.
- Communicate. Notify affected customers and remediate harm.
Accuracy: how do you prevent harmful hallucinations?
Hallucinations in consequential actions are governance failures. For high-stakes actions, grounding in approved sources is necessary and insufficient on its own. Add these safeguards:
- Multi-source validation requires corroboration from more than one source.
- Confidence thresholds let an agent act only above a set certainty level, for example 95%.
- Human review gates require human confirmation for certain decisions regardless of confidence.
- Deterministic fallback uses rule-based logic on critical paths instead of a large language model (LLM).
Multi-agent orchestration: how do you control agents that work together?
Multi-agent governance operates at the system level. Buyers should look for:
- defined rules for agent-to-agent communication
- system-level monitoring for emergent or cascading behavior
- circuit breakers and isolation that limit the blast radius of a failure
Human oversight: can people intervene when needed?
Effective platforms support graduated autonomy, which sets the level of human involvement by risk. They also provide emergency controls: immediate shutdown, override, and escalation paths.
Audit evidence: can the platform prove compliance automatically?
AI agent governance must produce evidence on demand. The platform should generate:
- an agent inventory: which agents exist, what they do, and who owns them
- decision logs with full provenance for consequential decisions
- policy enforcement records showing blocked guardrail violations
- fairness monitoring reports over time
- incident records covering root cause, remediation, and outcome
Buyers should also check support for recognized frameworks such as ISO/IEC 42001 (the international standard for AI management systems) and the NIST AI Risk Management Framework (AI RMF).

How does Artemis, the Kore.ai Agent Platform, govern AI agents?
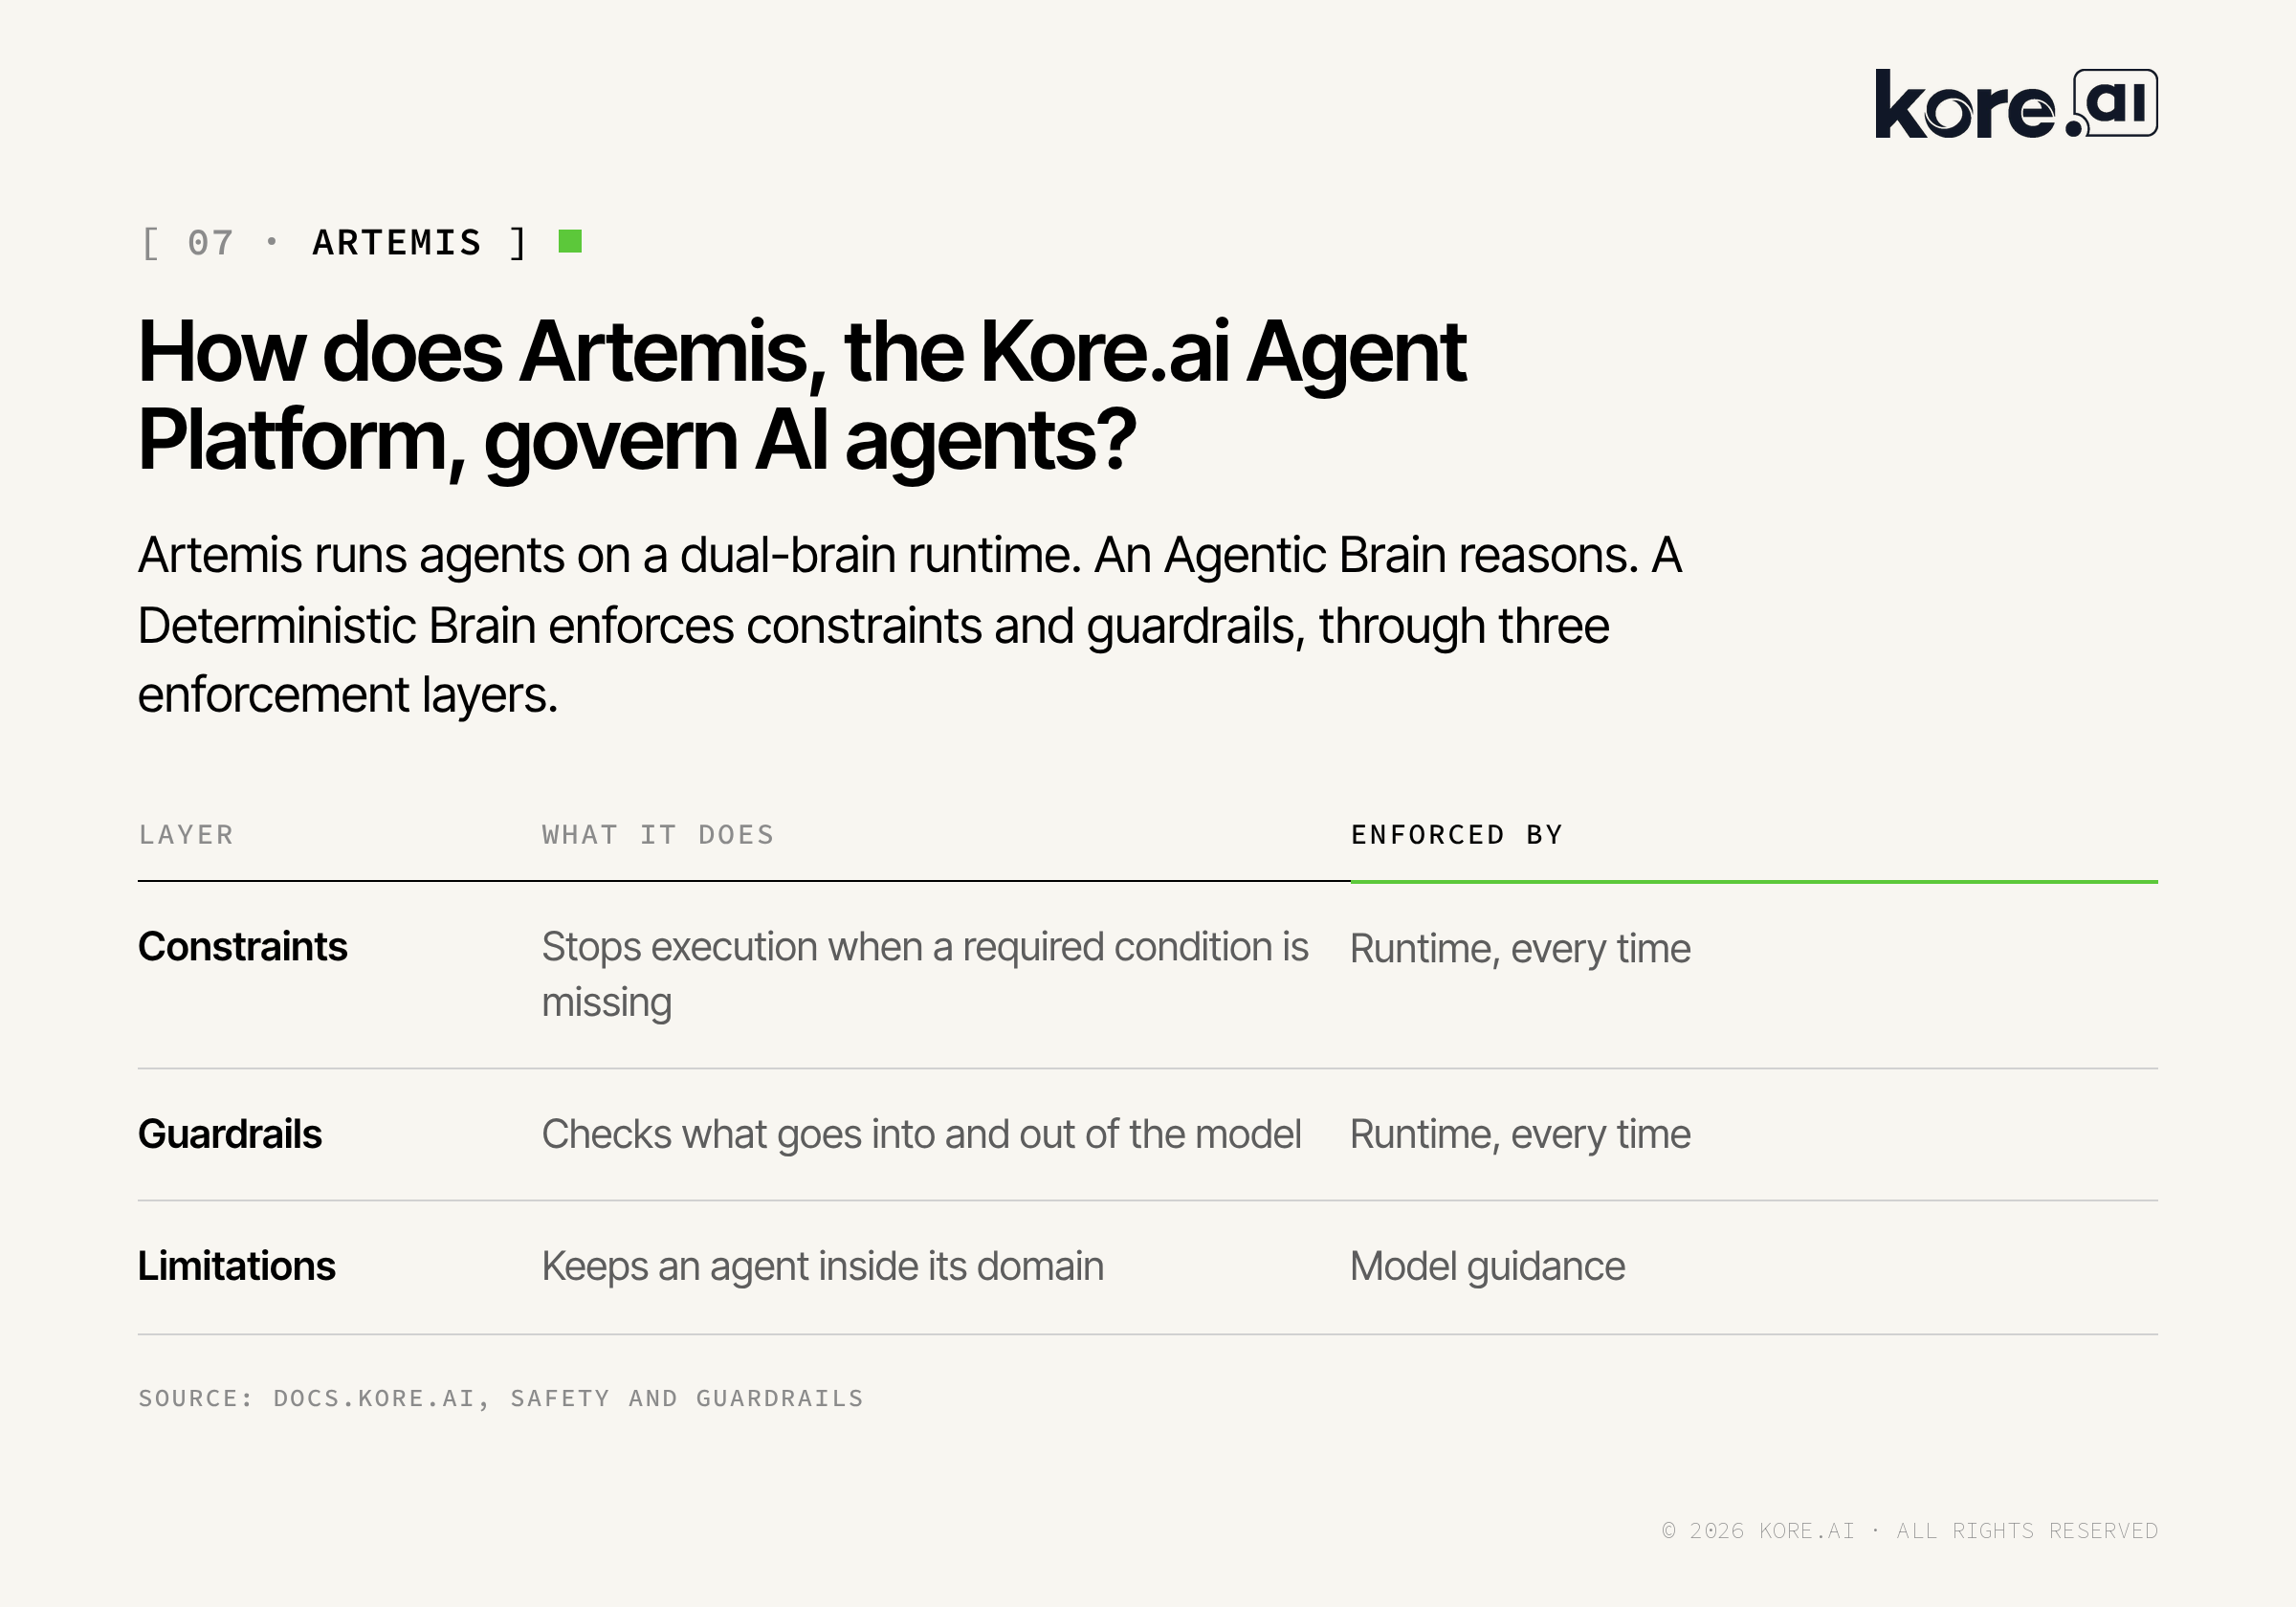
Artemis, the Kore.ai Agent Platform, builds governance into the agent runtime. Agents are defined in Agent Blueprint Language (ABL), compiled and validated before deployment, and run on a dual-brain runtime: an Agentic Brain that reasons and a Deterministic Brain that enforces constraints and guardrails. Every decision leaves a structured trace, so a team can reconstruct any session after the fact. (Kore.ai docs: Dual-brain architecture)
What enforcement layers does Artemis use?
Artemis controls agent behavior with three enforcement layers (Safety and guardrails):
Where do Artemis guardrails run?
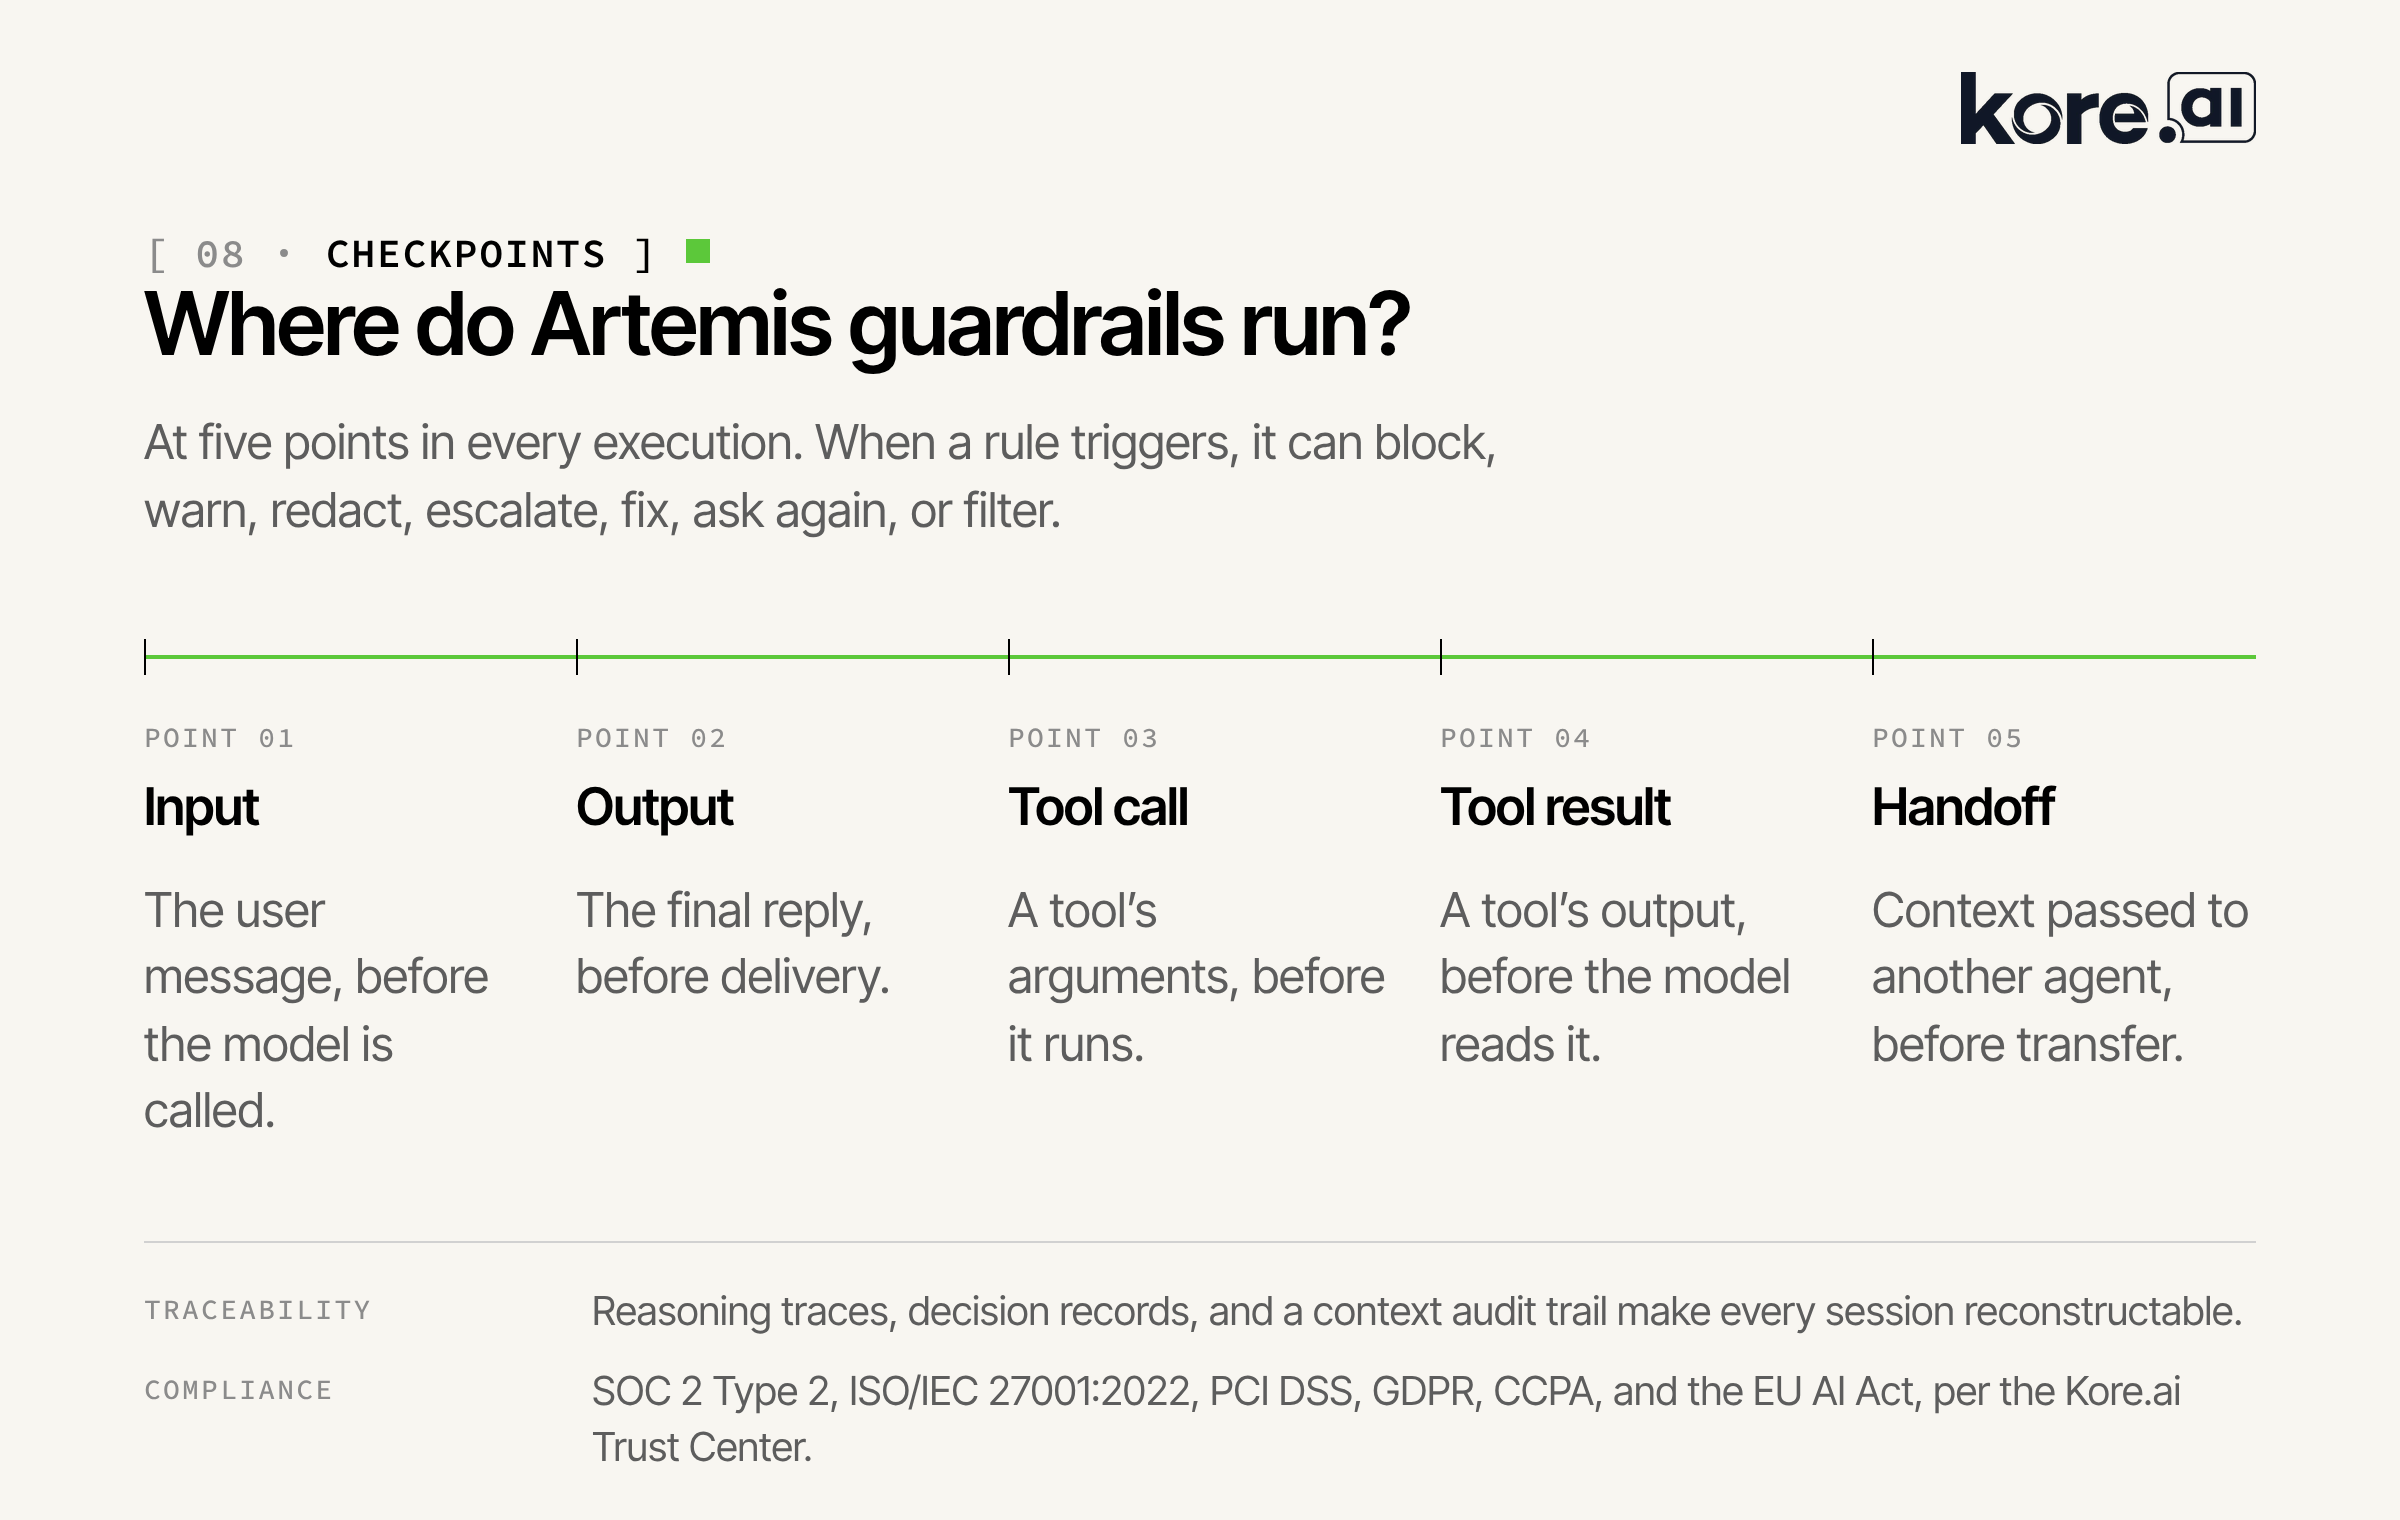
Artemis guardrails check five points in an agent's execution:
- Input: the customer's message, before the model is called.
- Output: the final reply, before it is delivered.
- Tool call: a tool's arguments, before the tool runs.
- Tool result: a tool's output, before the model reads it.
- Handoff: the context passed to another agent, before the transfer.
When a rule triggers, it can block, warn, redact, escalate, fix, ask again, or filter. Policies apply to a whole project or to one agent, and teams manage them in the UI or as code in ABL. Each policy has a fail mode: Closed blocks execution if a guardrail check fails or times out, and Kore.ai recommends it for compliance checks. The default, Open, lets content through on a provider failure. (Safety and guardrails)
How does Artemis make agent decisions traceable?
The Artemis runtime records three kinds of trace data. Together, they make every agent decision reconstructable (Dual-brain architecture):
- Reasoning traces capture every agent step, model call, and tool result.
- Decision records capture every routing choice, constraint check, and guardrail evaluation.
- The context audit trail captures what data each part of the runtime was working with at the moment of each decision.
How does Artemis protect personal data?
Artemis detects and redacts personally identifiable information (PII) with built-in and custom patterns, and controls how PII appears to each consumer: users, tool inputs, tool outputs, and logs. Large language models never receive plaintext PII. The platform replaces detected values with a stable token before text reaches the model. Credential and secret scrubbing is always on. (PII protection)
How does Artemis control what reaches production?
Artemis moves each release through development, staging, and production environments. Published versions are immutable, and the compiled agent is versioned and pinned to its deployment. A Strict production approval policy requires an approver other than the publisher. (Deployment)
What else supports governance in Artemis?
- Audit logs record logins, API key and credential changes, agent deployments, configuration changes, and channel connection changes. (FAQ)
- Circuit breakers halt calls to a failing tool endpoint or model provider after a set number of consecutive errors, which stops cascading failures. (Tools reference)
- Multi-agent orchestration uses supervisor routing with explicit delegate, handoff, and escalate steps, and handoff guardrails check context before it moves between agents.
- AI content disclosure flags each AI-generated message, so client apps can show users when they are talking to an AI agent. (AI content disclosure)
- Human escalation routes a conversation to a person when an agent reaches its limits.
- Compliance programs listed on the Kore.ai Trust Center include SOC 2 Type 2, ISO/IEC 27001:2022, PCI DSS, GDPR, CCPA, and the EU AI Act.
What results do enterprises see from built-in governance?
- Faster deployment. The first agent defines the governance patterns. Later agents reuse them.
- Less manual evidence work. Traces, decision records, and audit logs are generated by the platform.
- Faster approvals. Proven controls help legal, security, and compliance teams sign off sooner.
A real-life example
A global wealth management company with 120,000 employees runs its AI agents on Kore.ai's AI for Work solution and Agent Platform. Employees have built more than 2,600 agents with the platform's no-code-to-pro-code builder. Every agent includes built-in compliance checks: retrieved information passes through them before it reaches an advisor.
The company's CRC Pre-Review agent checks communications against regulatory requirements. It cut review time from days to minutes. Across the deployment, the company reports more than 90,000 hours and over $5 million in annual efficiency savings. (Kore.ai customer story: Global wealth management leader scales agentic AI to 120,000 employees)
This is the citizen-developer pattern from the start of this guide, with governance in place: thousands of employee-built agents, each running inside the same compliance checks.
How should an enterprise get started with AI agent governance?
- Build an inventory of every AI agent, its owner, and its data access.
- Classify each agent by risk, using the EU AI Act categories where they apply.
- Set runtime guardrails and human approval points for high-risk actions.
- Turn on decision provenance and audit logging before scaling.
- Assign a named owner for governance across legal, security, and the business.
Conclusion: governance is what lets AI agents scale
AI agent governance makes production deployment of autonomous agents possible. Regulation is tightening, courts are testing liability, and agent systems are growing more connected. Runtime guardrails, continuous monitoring, and decision provenance let teams detect, explain, and fix issues quickly, which builds the trust that approvals depend on.
Next step: Explore how Artemis builds governance into every agent, or talk to an expert.
FAQ
1. How do you manage AI governance inside automated workflows?
Enforce guardrails and data access controls at runtime, monitor every agent action, and keep humans able to intervene at machine speed.
2. Why do multistep AI automations need an audit trail?
An audit trail lets teams reconstruct each agent decision and action, which regulators and internal reviewers need when automation acts autonomously.
3. Can AI workflows require human approval before taking action?
Yes. Governance can define human oversight points so agents pause for approval on specified actions, especially high-risk or consequential ones.
4. What makes an AI review workflow transparent?
Traceability: logged inputs, decisions, tool calls, and outcomes that reviewers can inspect and explain after the agent has acted.
5. How should compliance-heavy industries govern AI workflow automation?
Combine runtime guardrails with continuous evaluation, drift management, and regulatory evidence generation, so every automated decision remains traceable.
Share
Tags